Cybersecurity Governance for Government & Critical-Infrastructure Leaders
What ministers, board members and directors-general must know about cyber risk: governance, accountabilities, incident response and protecting critical systems in energy, banking and telecoms.
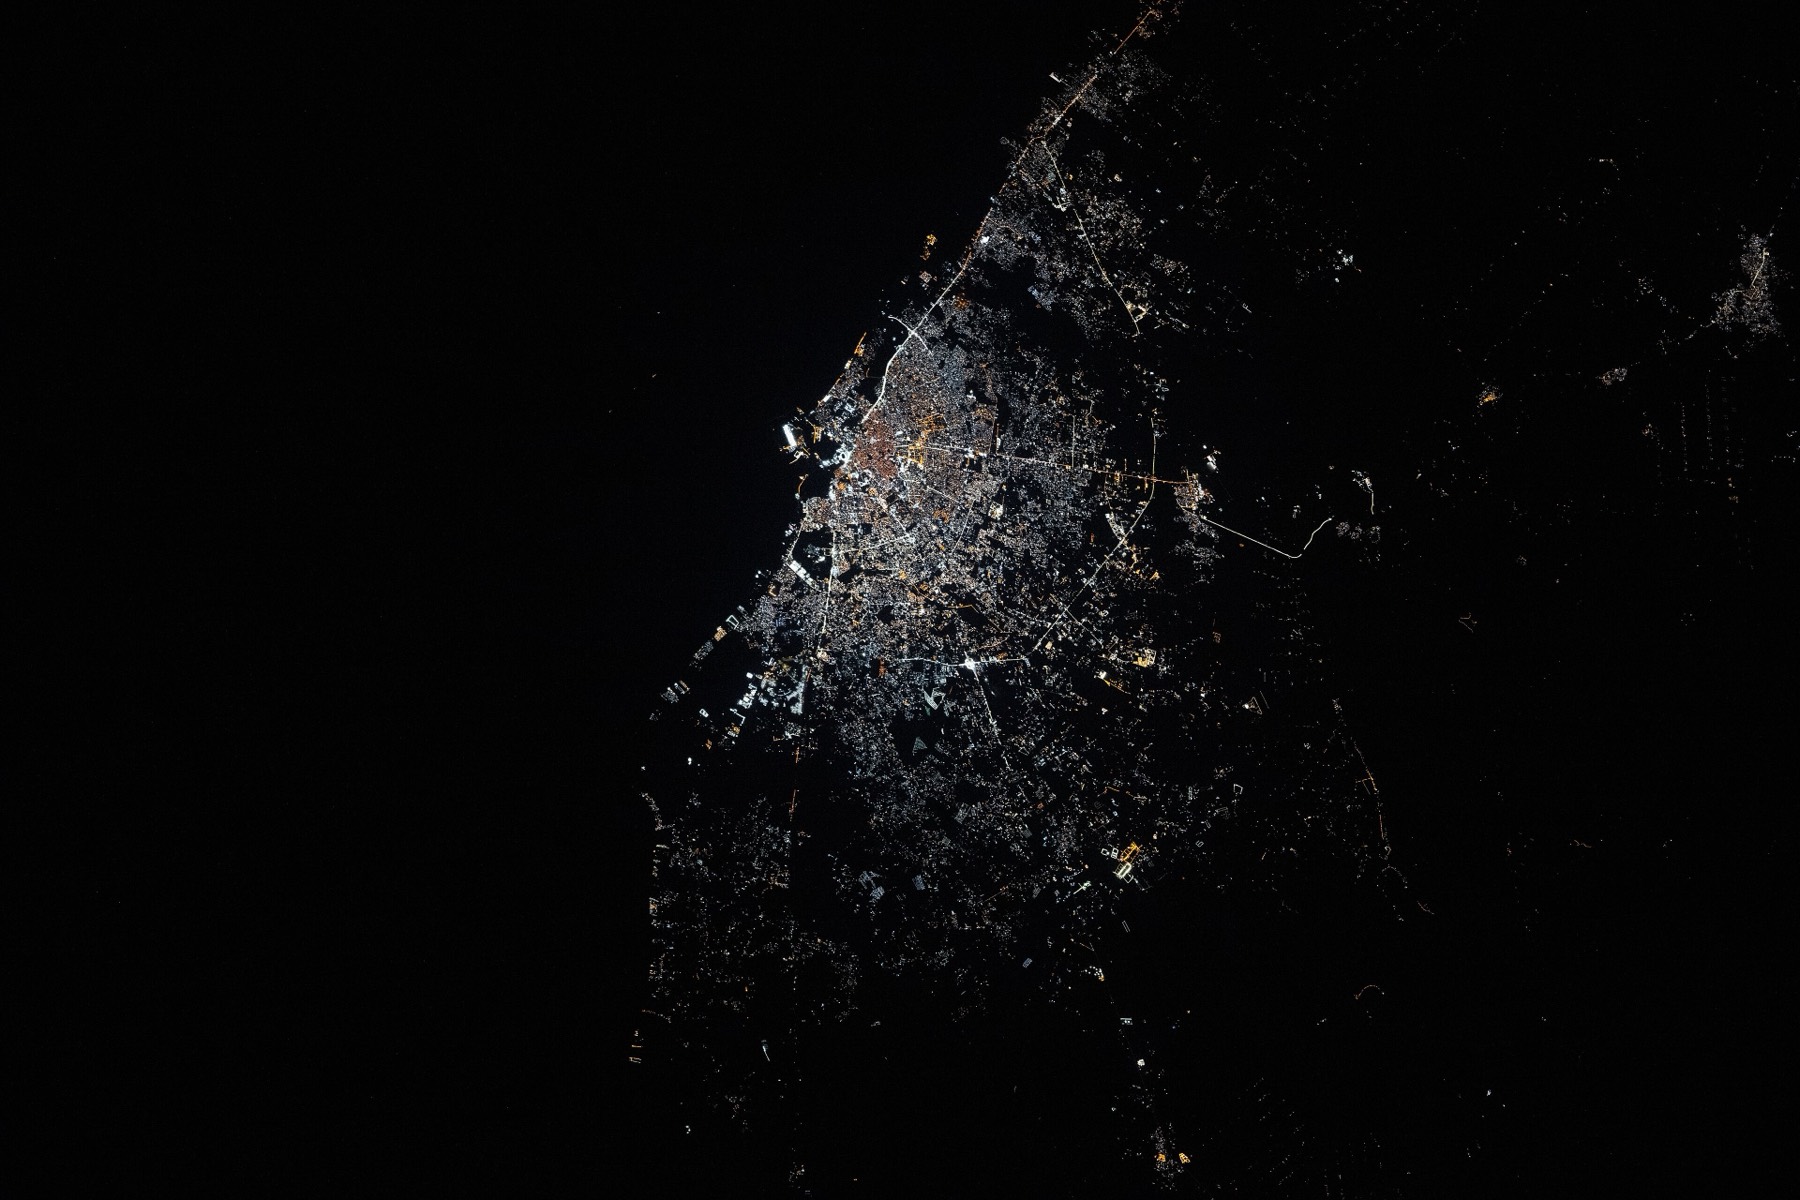
Benghazi from orbit
Programme overview
For non-technical leaders, translating cybersecurity into governance and investment decisions: the threat landscape, NIST and ISO 27001 frameworks, leadership's role in incident response and a leadership-room cyber-crisis simulation.
Learning Objectives
- Understand the cyber threat landscape for government and critical infrastructure.
- Define cyber-governance responsibilities at leadership level.
- Assess institutional maturity against NIST and ISO 27001.
- Lead the response to a major cyber incident.
Target Audience
- Ministers, deputy ministers and board members.
- Directors-general in energy, banking, telecoms and utilities.
- Heads of risk, compliance and internal audit.
Program Curriculum
- Module 1
Day 1: Cyber risk as a governance matter
- The threat landscape: attacks on governments, banks and energy
- Leadership and board accountability
- Module 2
Day 2: Frameworks, maturity and investment
- NIST and ISO 27001 in leadership language
- Maturity assessment and investment priorities
- Module 3
Day 3: Incident and crisis response
- Response, communication and recovery plans
- Simulation: a cyber attack on a government body